Checks and profiles
Import profiles and run scheduled audits with live logs
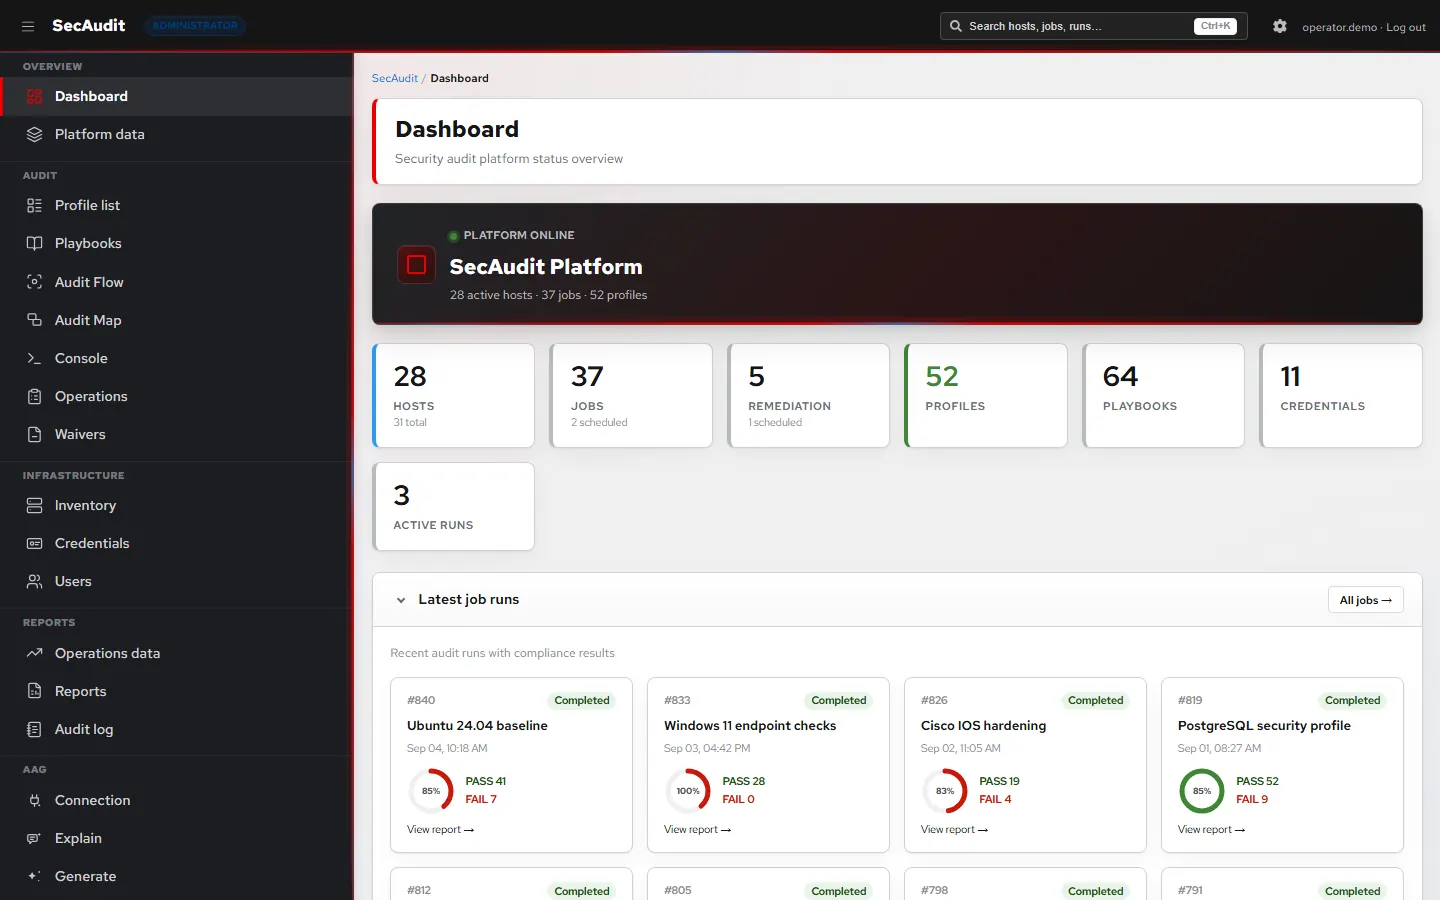
SecAudit Platform is an on-prem workspace for infrastructure security audits. Discover hosts with AuditFlow, run compliance checks, remediate findings, and verify the results
Capabilities
For security teams managing Linux, Windows, and network devices
Import profiles and run scheduled audits with live logs
Scan network ranges, identify hosts, and match each host to the right profile
Audit switches and routers, then generate vendor-specific remediation commands for review
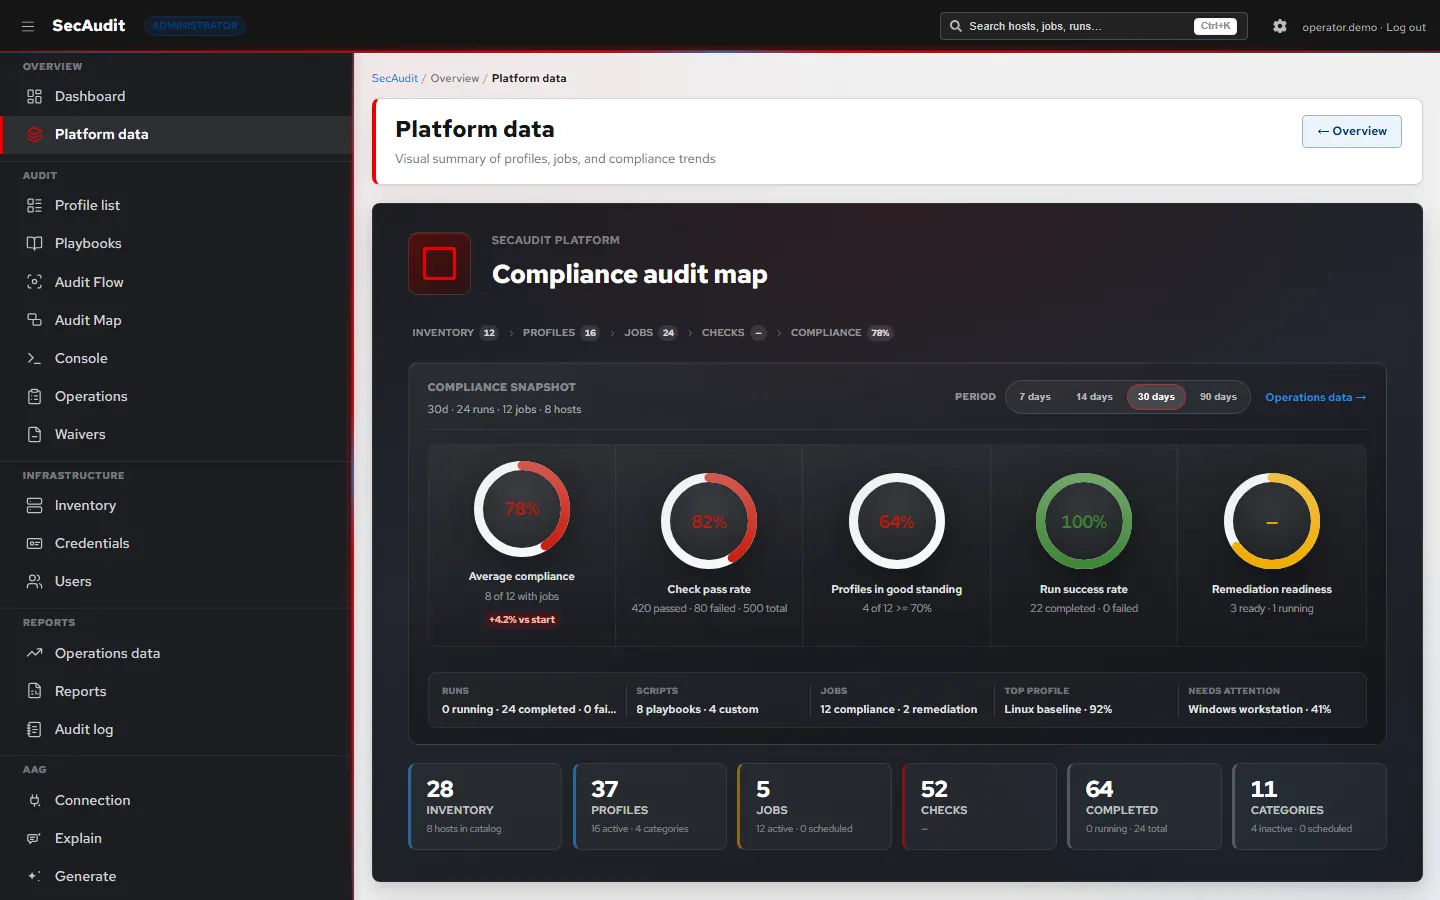
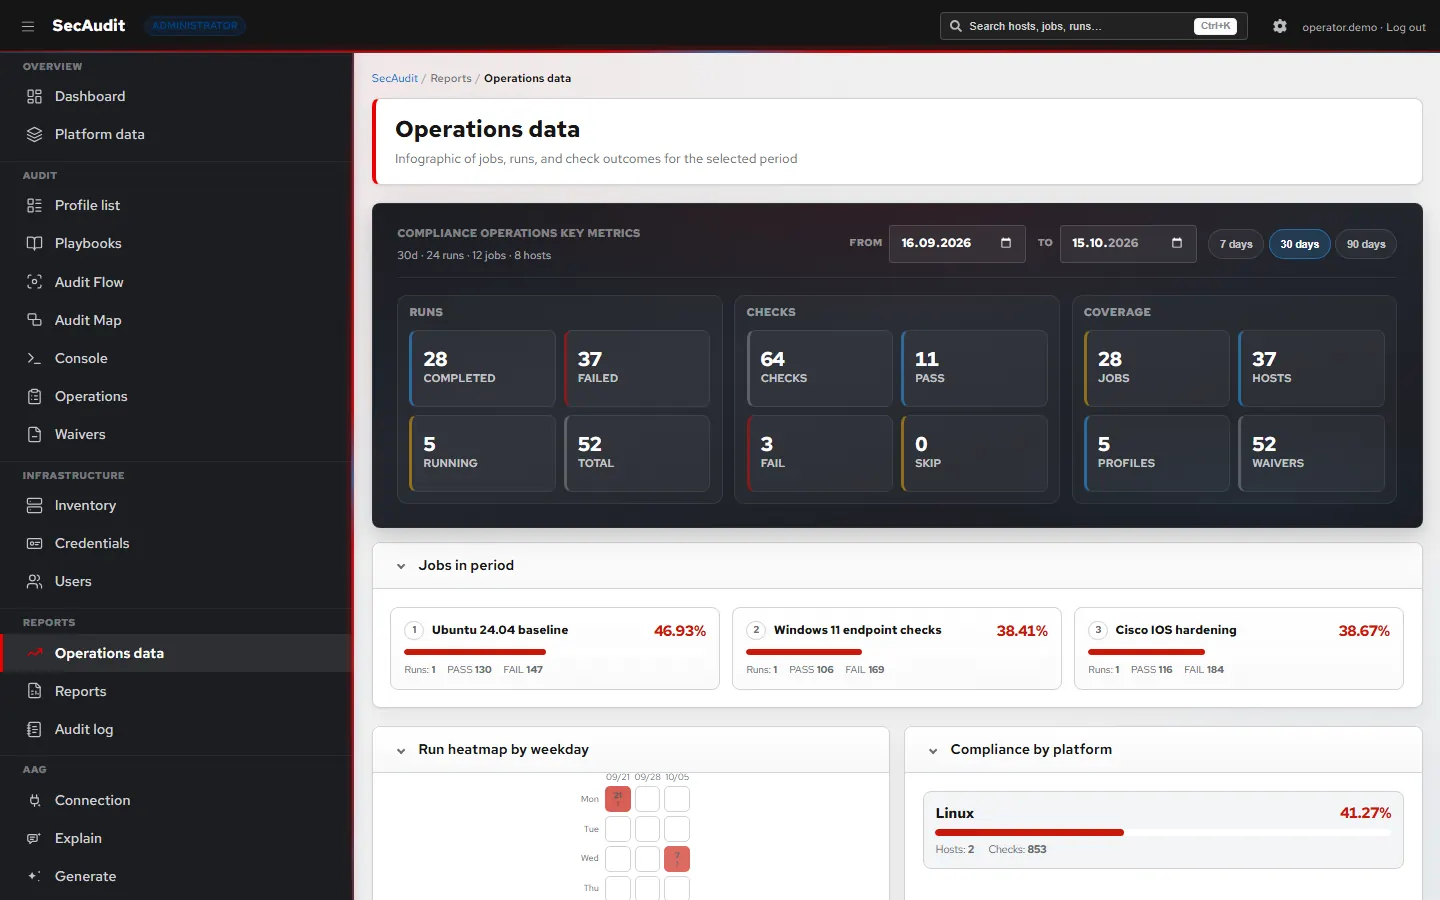
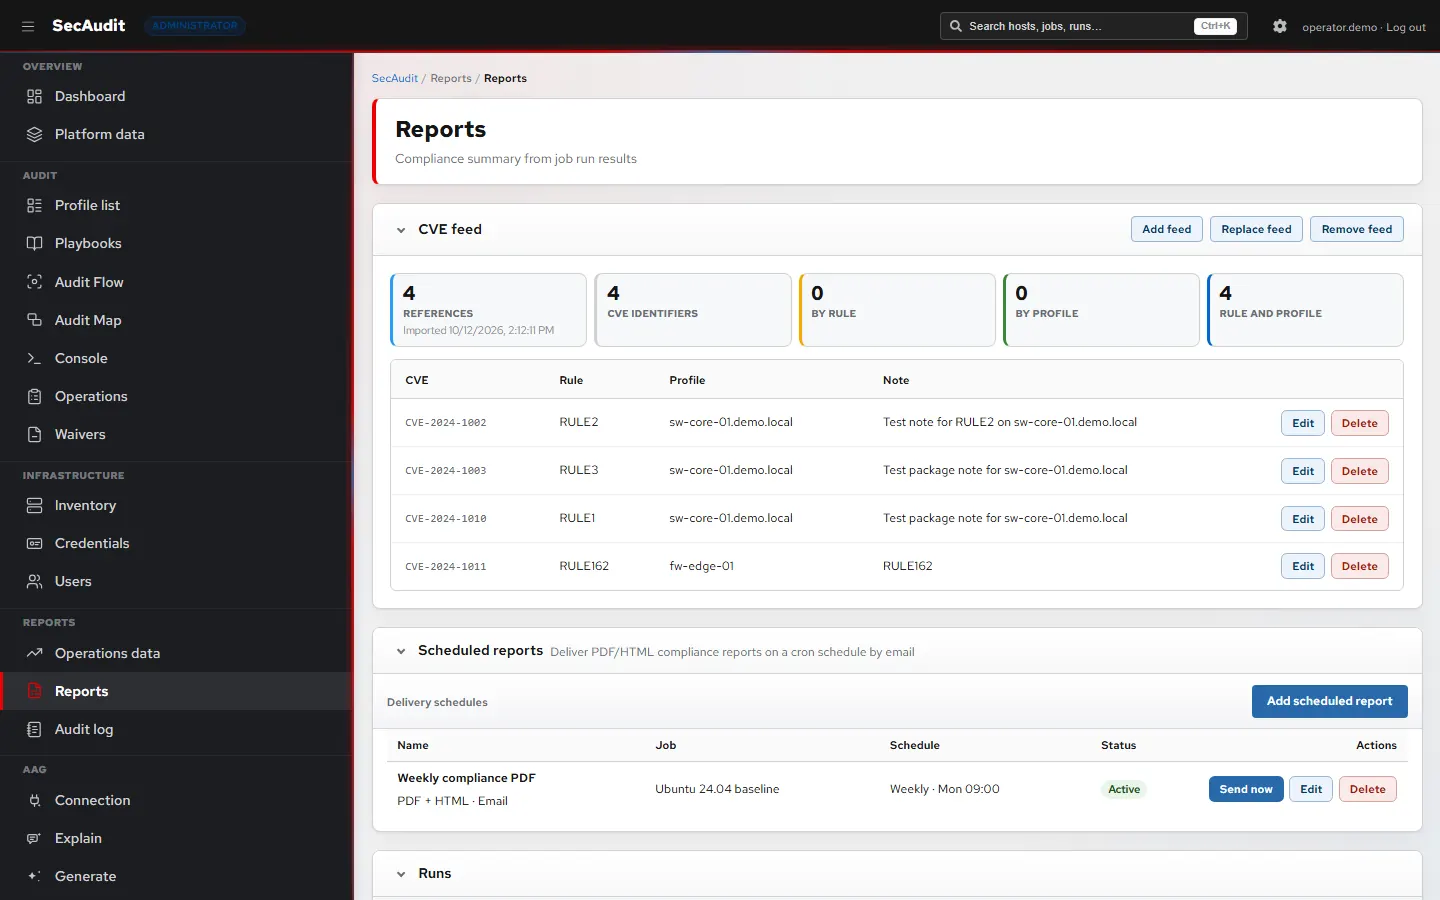
Export reports, compare runs, and track compliance over time
Turn failed checks into remediation jobs, then re-audit to verify the changes
SSO, object-level access control, encrypted credentials, and an audit trail of key actions
Platform UI
Screens from the SecAudit console — posture overview, guided audits, live job monitoring, and executive reporting
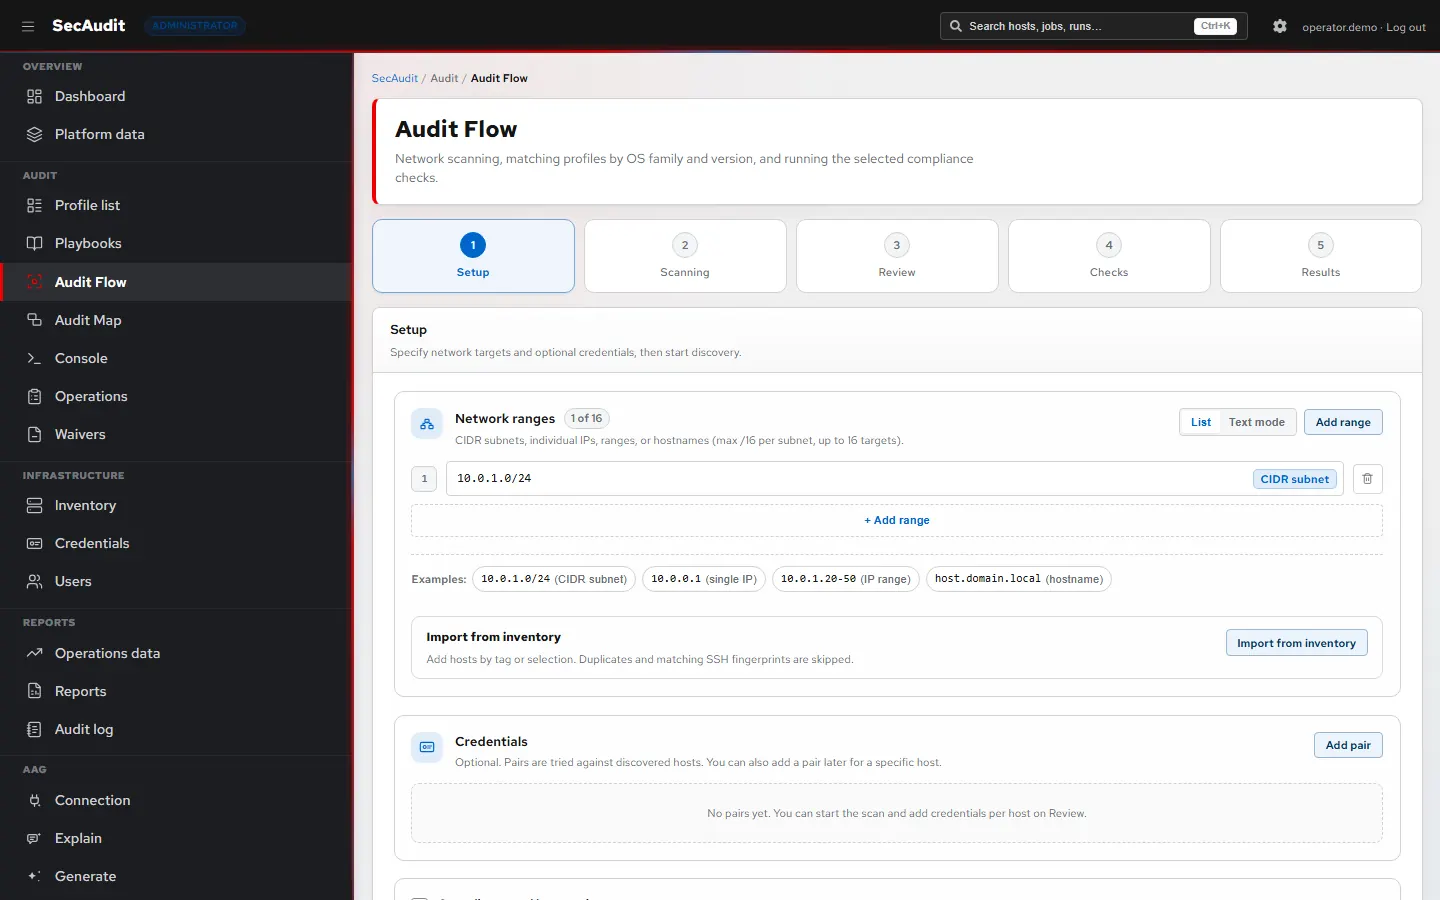
Scan network ranges, identify hosts, and match each host to a baseline profile
View details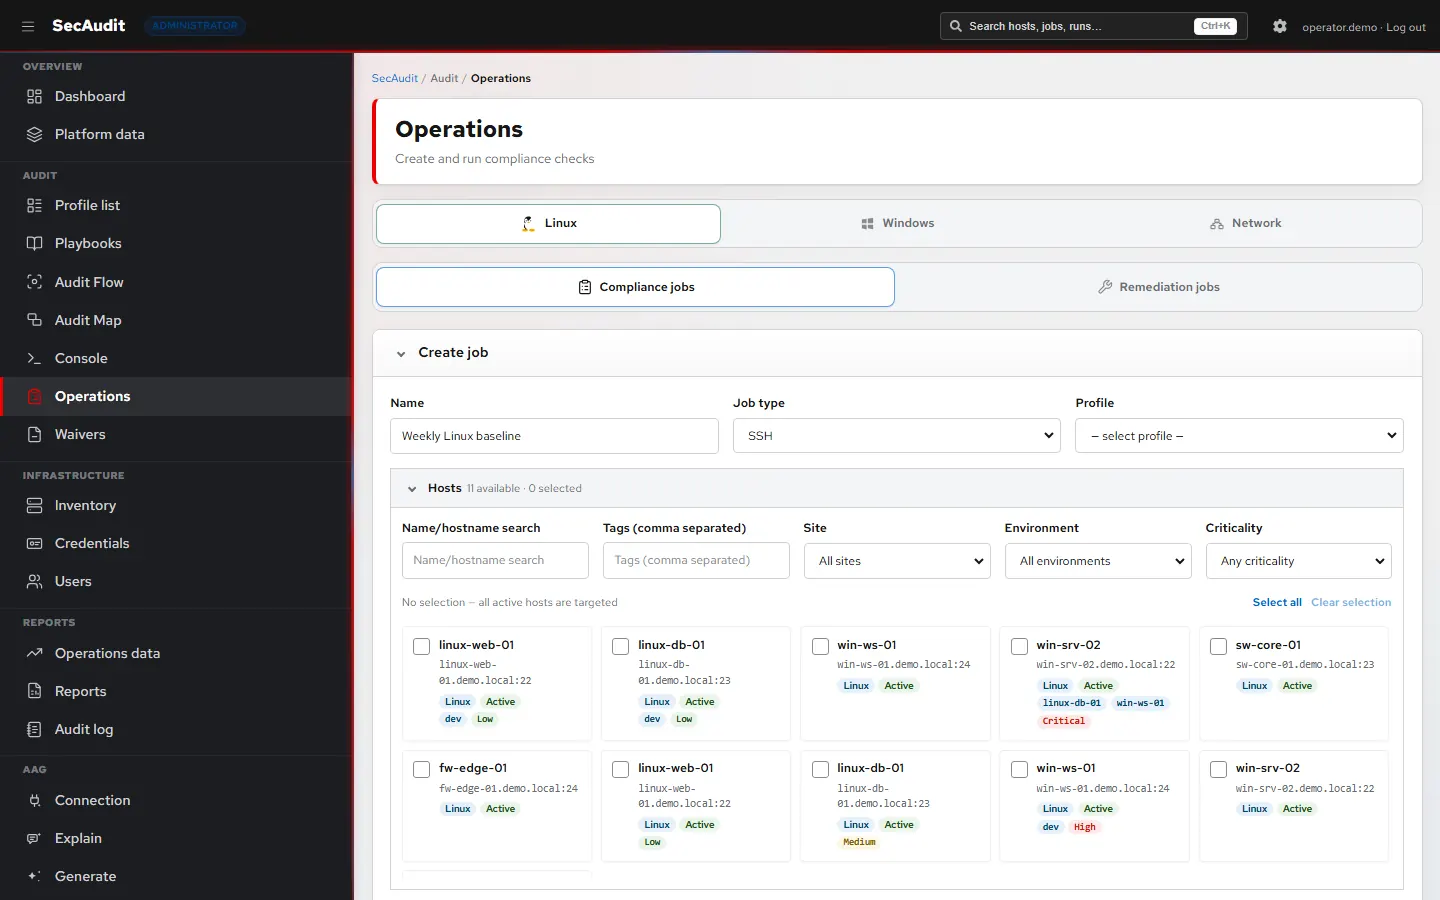
Select target hosts, launch compliance jobs, and monitor execution in real time
View details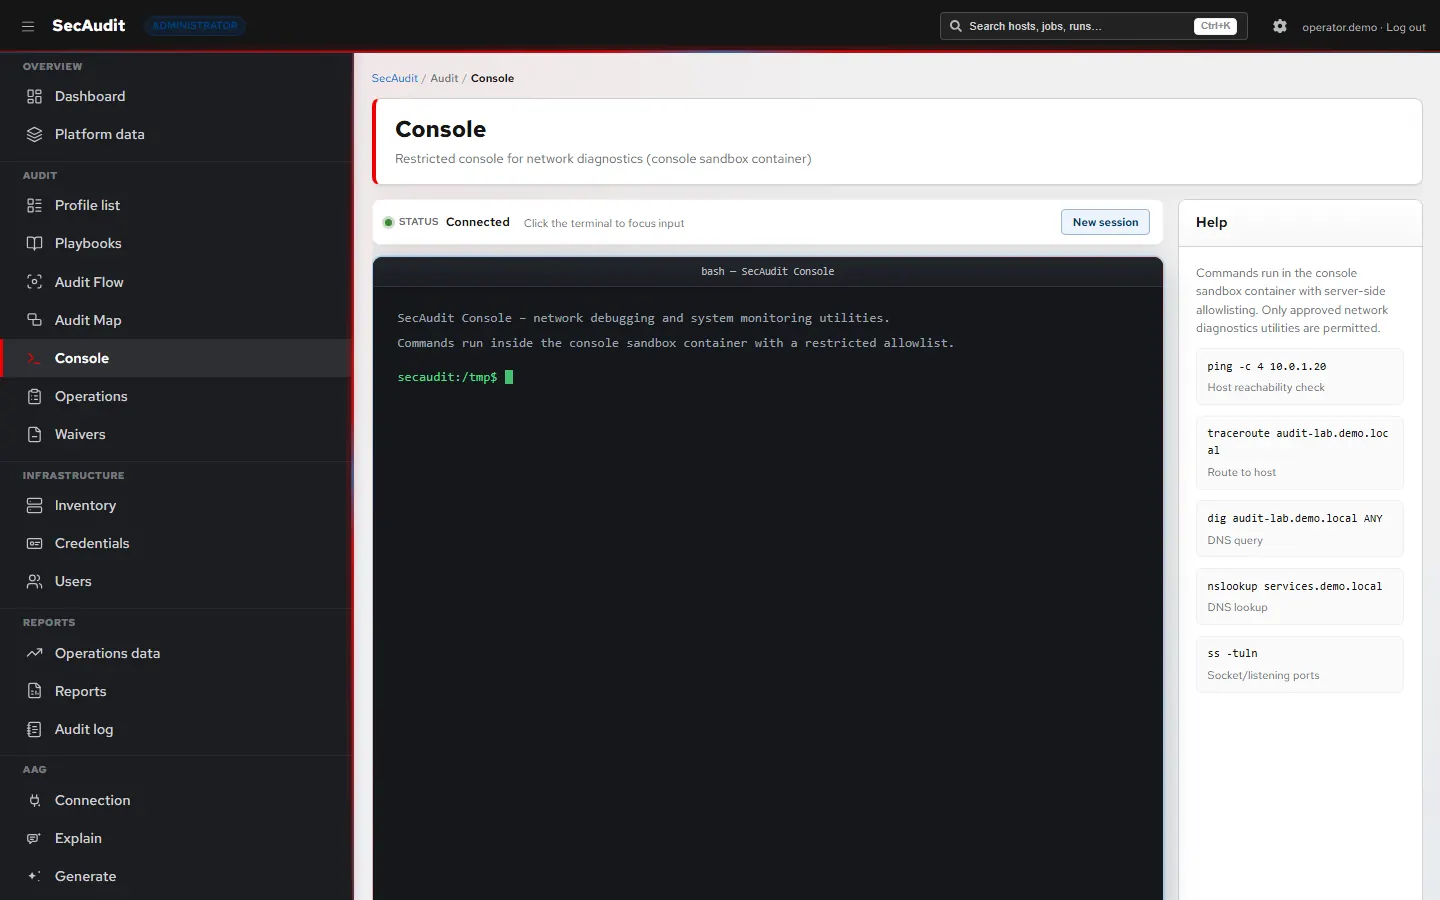
Run ad hoc checks with an embedded editor and live command output
View details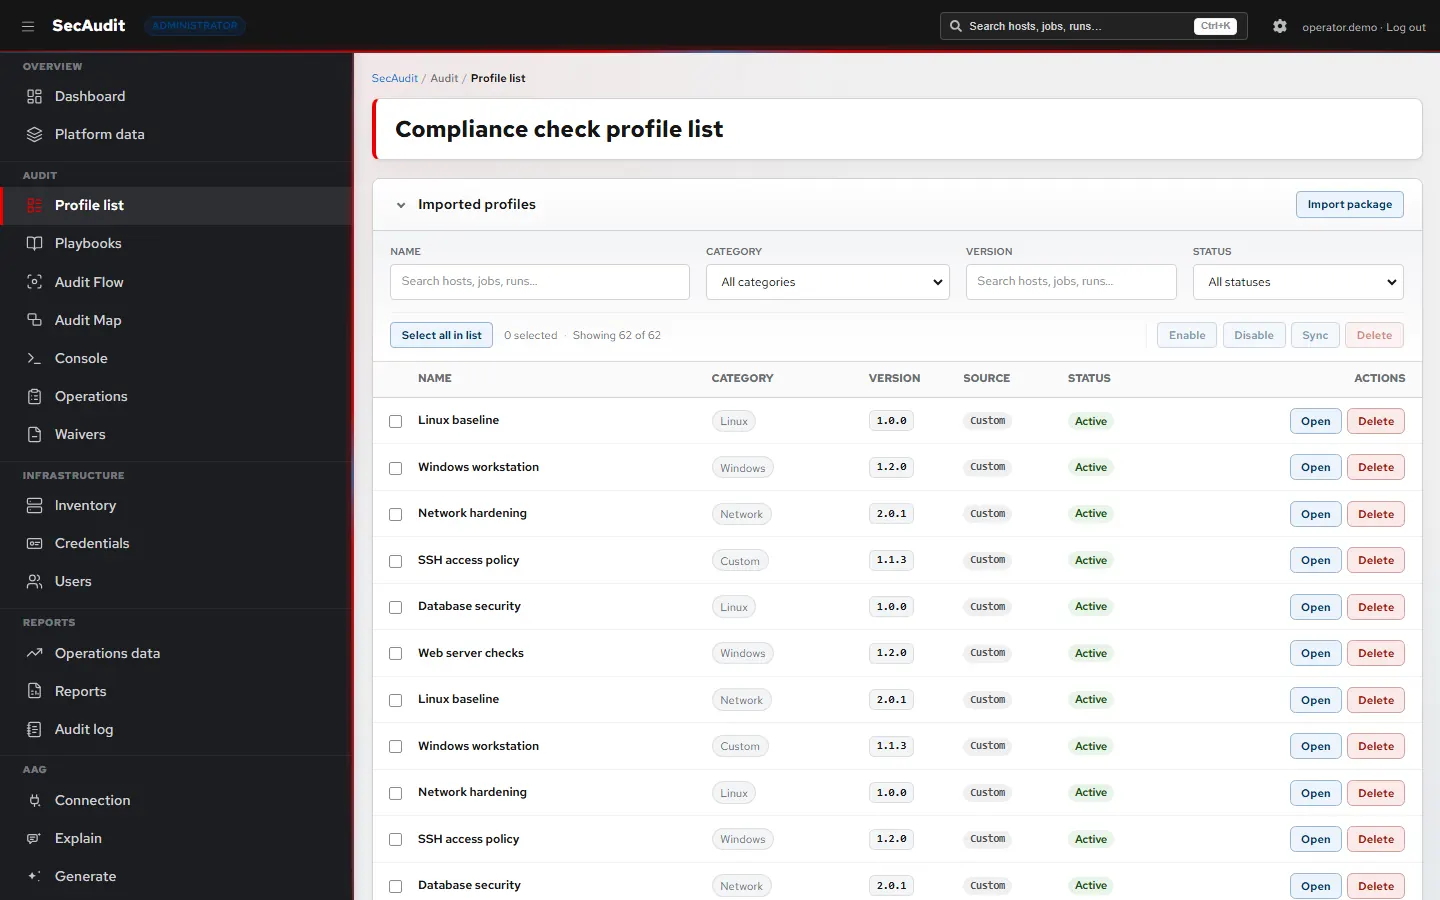
Browse imported and custom profiles by category and version, then edit them in one click
View detailsTechnology and trust
Five layers from the operator UI to managed systems — reliable job delivery, encrypted secrets, and full observability
Operators work in a single PatternFly interface with Keycloak OIDC or local authentication and object-level RBAC
View layerFastAPI provides REST and WebSocket APIs. secaudit_core manages profiles, AuditFlow, jobs, and reports
View layerPostgreSQL stores platform state. Redis Sentinel provides highly available queues, distributed locks, and scheduling
View layerCelery workers execute checks, remediation jobs, discovery scans, and scheduled tasks while streaming logs in real time
View layerAgentless SSH, WinRM, and network protocols connect to Linux, Windows, and network devices
View layerDeploy with Compose or Helm on your servers — keep operational data in your perimeter by default
Delivery failures retry automatically, and stalled jobs can be recovered
Encrypted credentials, object-level access control, and an audit trail of key actions
Metrics, traces, and operator dashboards help you monitor every run and investigate failures
Deploy SecAudit on your own servers with Docker Compose for labs or Helm for production. Source code is on GitHub under Polyform Noncommercial 1.0.0