Operators enter IP ranges or hosts, watch discovery progress, and review OS fingerprints as targets appear.
AuditFlow Discovery
Discovery WizardAuditFlow shortens onboarding from a CIDR list to matched compliance checks without a manual inventory spreadsheet.
Console path
secaudit.local/audit-flow 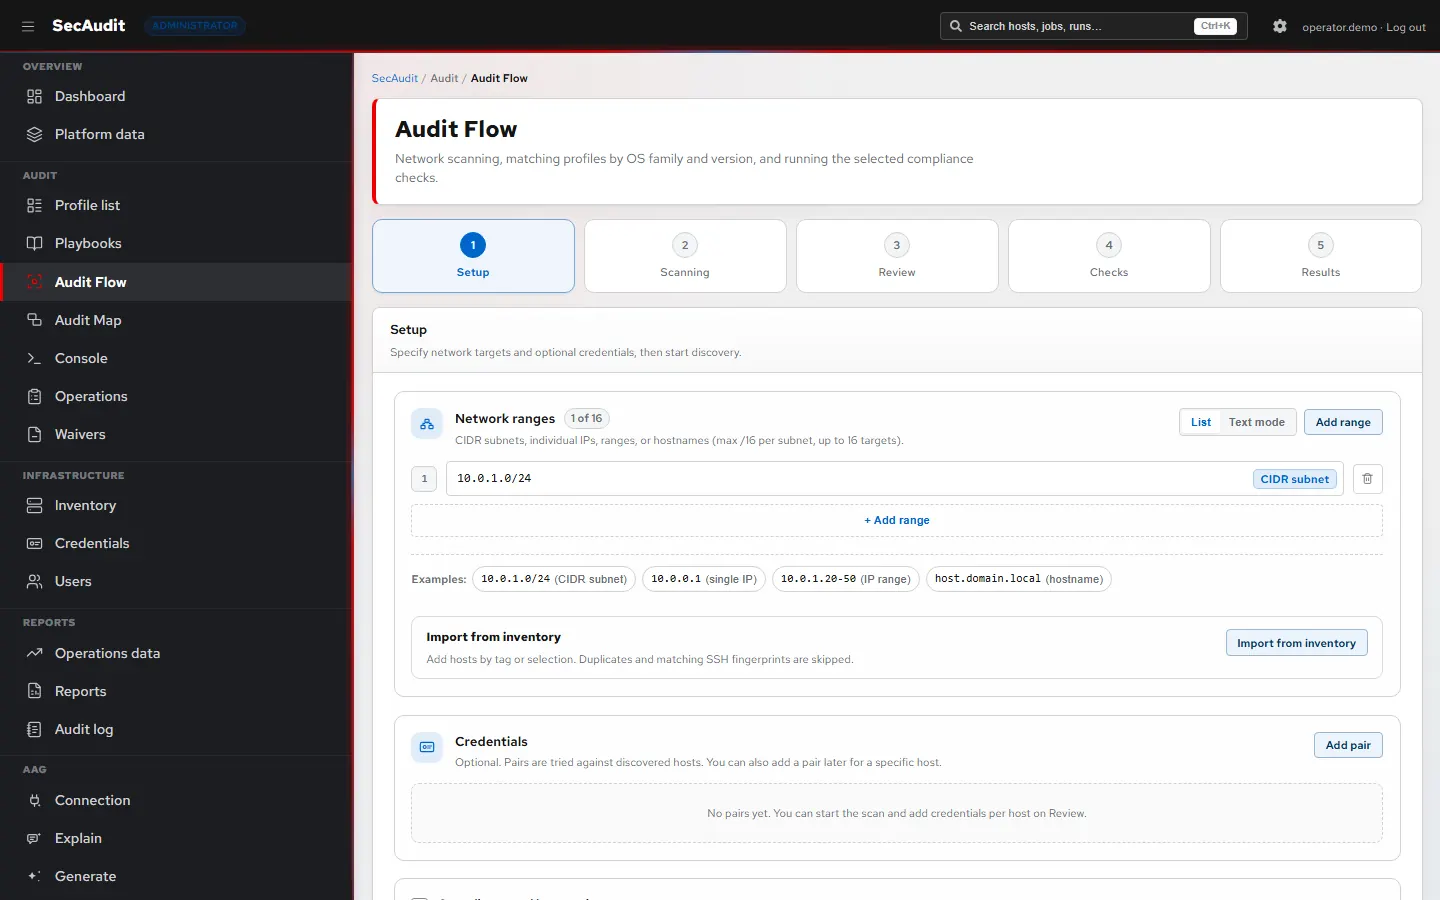
What you can do
-
CIDR / IP scanning with live discovery progress
-
OS fingerprinting and profile matching
-
Selective check launch after review
-
Optional inventory save and ephemeral credentials
SecAudit suggests matching CRE profiles for each host so teams can select checks instead of wiring jobs by hand.
Credentials can stay ephemeral for the session, and saving hosts to inventory remains optional.